TL;DR

Get smart everyday buys delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
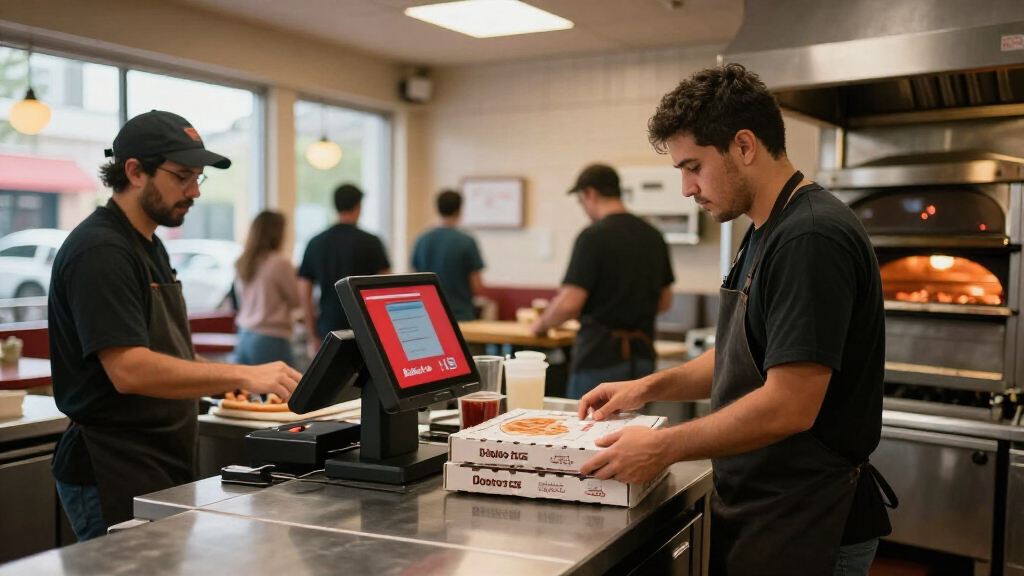
Dodo Pizza said hackers attacked its IT systems on September 27–28 and may have accessed some customers’ personal details and order information. The company says payment data is not stored in its systems, has notified Roskomnadzor and is reviewing the incident; a separate report of 68 million affected customers has not been confirmed by the company.
Dodo Pizza said hackers attacked its IT systems on September 27–28 and may have accessed some customers’ names, contact details, dates of birth and order information. The Russian pizza chain said it had blocked the attackers from accessing its data, notified Russia’s data protection regulator and begun an internal review.
The company said the potentially exposed information could include customers’ names, addresses, phone numbers, email addresses and dates of birth, as well as details of their orders. It has not specified how many customers may have been affected or confirmed that the listed categories were accessed in every case.
“We don’t store payment data — it’s safe,” the company said. Dodo Pizza also said it had notified Roskomnadzor, Russia’s communications and data protection regulator. The company’s account does not identify how the attackers entered its systems or when the breach was first detected.
The Telegram channel Baza reported that hackers obtained information on 68 million customers in several countries, including order histories covering the past 15 years. That figure and the reported scope have not been confirmed by Dodo Pizza in the information provided by Meduza. The company has not publicly stated how its internal review compares with Baza’s account.
Customer Data Across Multiple Markets
The incident could affect customers whose personal details and ordering records were held by a chain operating across several countries. If accessed, names and contact information could expose people to targeted scams or unwanted contact, while order histories can reveal patterns in where and when people order. These are potential risks; the company has not confirmed that the information was taken or misused.
Dodo Pizza said it had more than 1,527 pizzerias in Russia and 27 other countries as of fall 2026. That international footprint gives the company’s investigation a cross-border dimension, though it has not said which locations or customer groups may be involved. Its statement that payment data is not stored in its systems narrows the specific data risk it described, but does not establish the full scope of the incident.
Top picks for "pizza russian chain"
As an affiliate, we earn on qualifying purchases.
Attack Dates and Company Response
Dodo Pizza’s account places the attack on September 27–28, 2026. It said hackers may have accessed some customer data and that it had blocked their access. The company is now conducting an internal review; no findings from that review were included in the report.
The company said it notified Roskomnadzor. The available report does not give further details about the notification, including when it was sent or what information it contained. Meduza’s report was translated from Russian and reviewed by an editor, according to the publication’s note.
““We don’t store payment data — it’s safe.””
— Dodo Pizza
Breach Scope Still Under Review
The number of affected customers remains unknown. Dodo Pizza said some customers’ information may have been accessed but did not provide a count. Baza’s claim that data on 68 million customers and 15 years of order histories was obtained is a separate report and has not been confirmed by the company.
It is also unclear which specific records, countries or systems were affected, whether the attackers copied data, and whether any information has been published or used. The company has not described the method of entry or provided a timetable for completing its review.
Findings From the Internal Review
Dodo Pizza said its internal review is underway after it blocked the hackers’ access and notified Roskomnadzor. The next key information will be whether the investigation confirms that data was taken, what categories and customer groups were involved, and whether the reported scale is accurate.
The company has not announced a date for releasing further findings or described any direct notice to potentially affected customers. Until it provides more detail, the scope of exposure remains unresolved.
Key Questions
When did the attack on Dodo Pizza happen?
Dodo Pizza said the attack took place on September 27–28, 2026.
What customer information may have been accessed?
The company said the information may include names, addresses, phone numbers, email addresses, dates of birth and order details. It has not confirmed which records were accessed.
Were 68 million customers affected?
Baza reported that hackers obtained data on 68 million customers, but Dodo Pizza has not confirmed that figure in the account reported by Meduza.
Is payment information at risk?
Dodo Pizza said it does not store payment data and said it was safe. The company has not provided further technical details about the systems involved.
What is Dodo Pizza doing now?
The company said it blocked the hackers’ access, notified Roskomnadzor and is conducting an internal review. It has not announced when the review will be completed.
Source: rss
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.