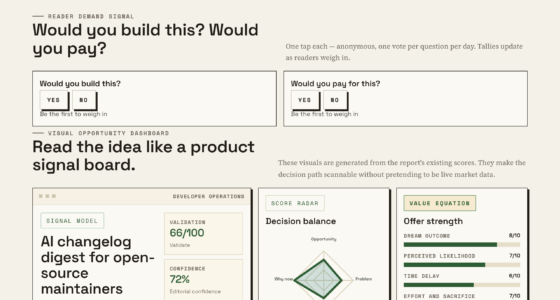
📊 Full opportunity report: Are Your Remote Work Devices Secure? Use This SMB Endpoint Checker on IdeaNavigator AI — validation score, market gap, and execution plan.

Get smart everyday buys delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
A new device security checker for remote SMB teams has been introduced, allowing voluntary installation to verify encryption, updates, and security settings. It aims to fill compliance gaps without invasive management tools. Deployment at early adopters will test its effectiveness for audits like SOC 2.
A new lightweight device security checker has been introduced for remote SMB teams, enabling voluntary installation to verify device security postures such as encryption, OS updates, and screen lock settings. This tool aims to address compliance gaps in environments with employee-owned and mixed hardware, a growing concern for SMBs facing security audits like SOC 2.
The tool, developed as a minimal viable product (MVP), involves a small agent that employees can install on their personal or company devices. It checks key security metrics—disk encryption, OS update status, screen lock activation, and password manager presence—and reports pass or fail results to a centralized dashboard. Unlike traditional MDM solutions, it does not allow remote control, making it less invasive and more suitable for employee-owned devices.
Marketed towards operations and security leads at SMBs, the solution is designed to fill a verification gap created by the increasing complexity of remote work. With regulatory frameworks like SOC 2 demanding proof of device security, this checker aims to provide documented evidence that can be shared with auditors, reducing the risk of non-compliance and potential breaches.
Initial validation involves deploying the tool at ten remote startups that are preparing for SOC 2 audits. The success of this deployment depends on high device-enrollment rates and acceptance of the reports by auditors as sufficient evidence of security posture. The company plans to offer per-device monthly pricing, with optional compliance report exports for paid tiers.
Why SMBs Need a Lightweight Device Security Check
This development matters because many SMBs lack the comprehensive device management infrastructure found in larger enterprises. As remote work becomes standard, companies face increasing risks from unmanaged personal devices that may lack essential security features. The new checker offers a simple, scalable way to verify device security without invasive management tools, helping SMBs meet compliance standards like SOC 2 and reduce breach risks.
By providing documented security posture reports, the tool can streamline audit processes and demonstrate due diligence to clients and regulators. Its low-overhead, voluntary installation approach makes it accessible for employee-owned devices, which are often excluded from traditional mobile device management (MDM) solutions due to privacy concerns.
device security compliance checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Compliance Demands and Remote Device Challenges
Remote teams increasingly rely on personal and aging hardware, including MacBooks, Windows laptops, and unmanaged smartphones, creating security vulnerabilities that are hard to verify. Traditional management solutions like MDM are often too invasive or impractical for employee-owned devices, leading to a verification gap in SMB environments.
Recent regulatory and client-driven security reviews, such as SOC 2, require documented proof of device security measures. However, many SMBs struggle to produce consistent, verifiable evidence, exposing them to potential compliance failures and security breaches. The introduction of a lightweight, voluntary device checker aims to address these issues by offering a simple, scalable solution tailored to SMB needs.
Early market validation involves deploying the tool at startups facing upcoming security audits, with success measured by device enrollment rates and auditor acceptance. This approach reflects a broader shift toward lightweight, non-invasive security verification methods suitable for diverse and unmanaged device fleets.
endpoint security verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Uncertainties About Adoption and Auditor Acceptance
It remains unclear how quickly SMBs will adopt this tool at scale and whether auditors will accept the generated reports as sufficient evidence of device security. The effectiveness of the tool in diverse hardware environments and its ability to meet different regulatory standards are still being tested. Further validation is needed to confirm its role in streamlining compliance processes and reducing security risks.
remote device security audit software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps in Deployment and Validation
The company plans to deploy the tool at additional SMBs preparing for SOC 2 audits, collecting data on device enrollment rates and report acceptance. They will also seek feedback from auditors to refine report formats and verification standards. Pending positive results, a broader rollout and potential feature enhancements—such as automated remediation guidance—are expected in the coming months.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does this device checker differ from traditional MDM solutions?
The checker is a lightweight, voluntary agent that only reports security posture metrics without remote control capabilities. It is designed to be less invasive and suitable for employee-owned devices, unlike traditional MDMs that often require full device management and control.
Will this tool work across different operating systems?
The initial focus is on common OSes like Windows and macOS, with potential expansion to mobile platforms depending on user feedback and technical feasibility. Compatibility details are still being finalized.
Can this tool help with compliance beyond SOC 2?
While primarily aimed at SOC 2 verification, the tool could potentially support other standards requiring device security evidence, such as ISO 27001 or HIPAA, depending on how reports are structured and accepted by auditors.
Is installation mandatory for all employees?
No, the tool is designed for voluntary installation. Adoption depends on company policies and employee willingness, which may impact overall effectiveness.
What happens if a device fails the security check?
The dashboard provides self-remediation instructions, such as updating the OS or enabling disk encryption, allowing employees to address issues without remote intervention.
Source: IdeaNavigator AI
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.